TL;DR
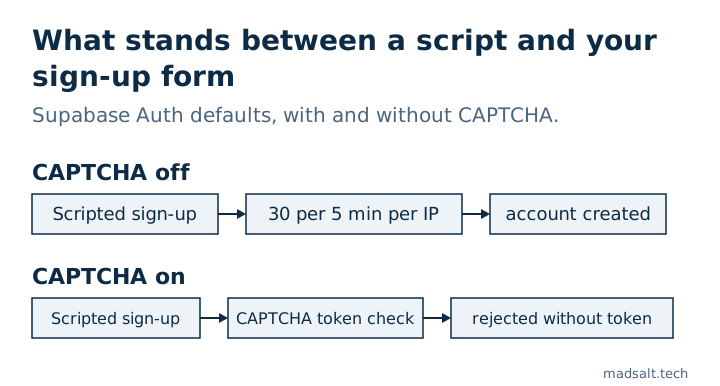
Without CAPTCHA, the only thing between a script and your sign-up form is Supabase Auth’s rate limit, which by default lets each IP address make 30 sign-up and sign-in requests per 5 minutes. Rate limits slow a single machine; they do not tell a person from a bot spread over many addresses. Supabase supports hCaptcha and Cloudflare Turnstile on sign-up, sign-in and password reset. Turn one on before launch, not after the first wave of fake accounts.
My free Supabase security checker reads a project’s Auth settings, and “CAPTCHA off for sign-up and sign-in” is one of its rules. It is a medium finding, not a critical one: nothing leaks, but the open door costs money and data quality.
What do Supabase’s rate limits allow?
Supabase’s rate limits guide, read on 23 October 2026, lists the defaults. Most are counted per IP address with a token bucket that allows short bursts:
| Endpoint group | Default limit | Counted by |
|---|---|---|
Sign-ups and sign-ins (/signup, /recover, /otp, /magiclink, /resend, /user) |
30 requests per 5 minutes, bursts up to 30 | IP address |
| Token endpoint (password, refresh token, PKCE) | 150 requests per 5 minutes | IP address |
| Emails sent with the built-in provider | 2 per hour | project |
| MFA challenge and verify | 15 per minute | IP address |
The local stack uses the same sign-up number: sign_in_sign_ups = 30 in the [auth.rate_limit] section of supabase/config.toml.
These numbers protect Supabase and your email quota. They are per IP, so traffic spread over many addresses passes each limit separately, and a quiet bot that stays under 30 requests per 5 minutes is never limited at all.
What does CAPTCHA add?
With CAPTCHA protection on, Supabase Auth expects a token from the CAPTCHA widget on sign-up, sign-in and password reset, and verifies it with the provider before doing anything else. Supabase’s CAPTCHA guide supports two providers:
- hCaptcha, with a site key in the frontend and a secret key in Supabase.
- Cloudflare Turnstile, which often runs without a visible challenge.
What it protects against in practice: fake sign-ups that fill your user table and your email sending quota, password guessing against the sign-in form, and password reset emails sent in bulk to addresses that never asked for them.
How do you turn it on?
- Create a site in hCaptcha or a Turnstile widget in Cloudflare and copy the site key and secret key.
- In the Supabase Dashboard, open Authentication → Bot and Abuse Protection, enable CAPTCHA protection, pick the provider and paste the secret key.
- Add the widget to every form that calls Auth and pass its token:
supabase.auth.signUp({ email, password, options: { captchaToken } }), and the same option on sign-in and password reset. - Reset the widget after each call, since a token is single use.
Turn it on in the Dashboard only when the frontend already sends the token: from that moment, Auth calls without a token fail, including your own forms. For the sign-in counter in your own Edge Functions, keep the state in Postgres, not in memory; why an in-memory counter never fires on hosted Supabase is in my Lovable app security checklist. Leaked passwords, the other half of sign-up hygiene, are in Supabase leaked password protection.
If you want a person to go through the whole app rather than one setting, I do a Supabase security audit with a keep, fix or rewrite verdict for each part.
My similar case
I applied the migrations of 1,170 public Supabase projects to fresh databases: of the 568 that ran cleanly, 134 (23.6%) had a table with RLS off that the public key could read and change. The method and queries are in the open-source Supabase study.
Seeing fake sign-ups? Write to me and we’ll lock down your auth settings.
Seeing fake sign-ups?
Tell me what you have now and what you need. I'll reply with the option I'd pick.
Write to me